SAP GRC & Security Services
SAP GRC helps you control who can do what in SAP, and then prove it to auditors. That is why SAPCorePath designs, implements and runs SAP GRC and SAP security. As a result, access stays safe and compliant.
SAP GRC that reduces real risk
Access risk grows quietly. For example, users change jobs, firefighter access stays open and new transactions land in old roles.
However, auditors expect clear evidence and fast answers. Therefore, good SAP GRC combines clean roles, working controls and simple reporting.
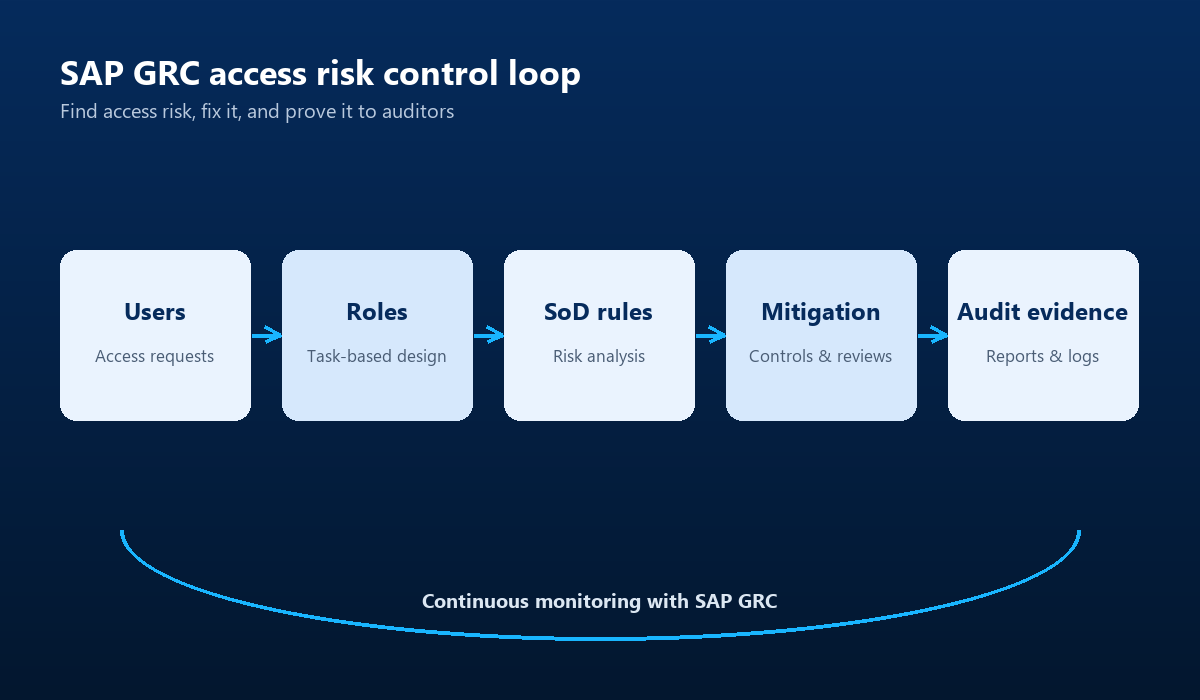
SAP GRC and security services we deliver
We cover everything from access risk analysis to automated controls. In short, we help you stay audit-ready.
We implement risk analysis, access requests, user access reviews and emergency access. Then we support them.
First, we design the rule set and run SoD analysis. Then we remediate and add mitigation controls.
We build clean, task-based roles for ECC, S/4HANA and Fiori. As a result, roles are easy to maintain.
We set up automated and manual control monitoring. In addition, we collect testing evidence for audits.
We implement Identity Access Governance for cloud and hybrid landscapes. Also, we connect it to your SAP systems.
We review security parameters, critical authorisations, RFC set-up and security notes. Consequently, attack surface shrinks.
Our approach to access risk
First we find the risk. Then we fix the root cause. Finally, we keep it under control.
First, run access risk analysis on users and roles.
Next, agree the rule set, role concept and controls.
Then fix conflicts and remove excess access.
After that, set up GRC workflows and reviews.
Finally, support audits and keep controls working.
Evidence you can show your auditors
- Access risk analysis report
- SoD rule set
- Remediation plan
- Role design concept
- Mitigation control library
- User access review process
- Emergency access procedure
- Audit evidence pack
Backed by the whole SAP stack
We combine GRC, security and Basis experience. As a result, controls work at the technical level as well as on paper.
We also link access reviews with licensing. For example, removing unused access can lower licence costs too.
For product documentation, visit the SAP Help Portal.
SAP GRC questions, answered
Here are common questions from audit, risk and IT teams.
What is SAP GRC Access Control?
It is SAP software for access risk. For example, it analyses risk, manages access requests, runs user access reviews and controls emergency access.
What is segregation of duties?
It means no single user can complete a sensitive process alone. For instance, one person should not create and pay a vendor. GRC software checks this with a rule set.
Do we need GRC software to manage access risk?
Not always. First, we can run a risk analysis and clean up roles. However, GRC automation makes control much easier to sustain.
Can you help us prepare for an audit?
Yes. First, we review controls and fix gaps. Then we prepare clear evidence before the audit starts.
Know your SAP access risk before the auditors do
Start with an SAP access risk review. As a result, you will see the main conflicts and a practical fix plan.